Computer worms can spread quickly across networks and devices, causing slowdowns, data loss, and security breaches. This guide offers practical, step-by-step instructions for identifying, removing, and preventing worm infections on Windows PCs and other common systems. The focus is on safe, proven methods that minimize risk to your data and improve ongoing protection.
The goal is to help users recover control of their systems with actionable steps, clear warnings, and practical tools that fit typical home and small-business setups. Readers will learn a structured approach that blends offline and online scanning, cleanup, and prevention strategies.
Quick Answer
Isolate infected devices, boot from a clean recovery tool or offline scanner, run comprehensive malware removal software, update all security layers, and reset network credentials after confirming cleanup. Regular backups and ongoing monitoring are essential to prevent reinfection.
What You’ll Need
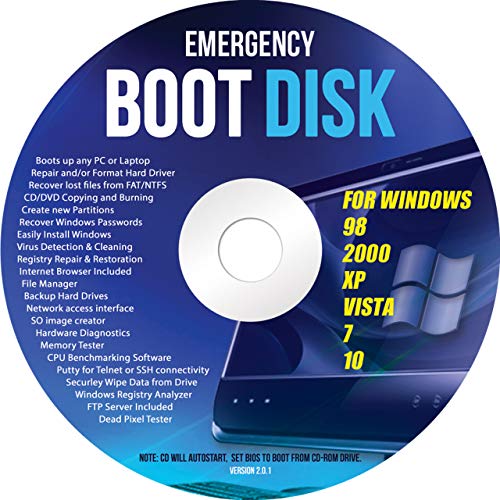
- Bootable USB malware removal rescue disk
- Windows antivirus software malware removal
- Offline malware scanner bootable USB
- Malware removal tool for PC
- Network security firewall appliance antivirus protection

Before You Start
Prepare a clean recovery environment and a safe backup plan. Disconnect affected devices from the network to contain the spread until cleanup is complete. Ensure you have another working device to download tools and create bootable media. Time estimates vary; plan for several hours for a thorough scan and cleanup. Be aware that worms can disguise as legitimate processes, so proceed with caution and verify each finding before removing.
Step-By-Step: How To Get Rid Of Computer Worms
- Identify symptoms such as unusual network traffic, new startup entries, or unexplained processes in Task Manager.
- Isolate suspect machines by disconnecting Ethernet/Wi‑Fi from the router to prevent further propagation.
- Create a bootable recovery environment using a bootable USB malware removal rescue disk.
- Boot the infected PC from the USB drive and run the offline malware scanner bootable USB to detect threats outside the operating system.
- Run a full scan with Windows antivirus software malware removal or a trusted malware removal tool for PC to purge malicious components.
- Remove detected threats, then restart and boot normally. Check for residual symptoms and re-scan if necessary.
- Update your operating system and all software to the latest security patches.
- Reset network credentials (Wi‑Fi passwords, router admin password) and apply strong, unique passwords.
- Reconnect devices in a controlled manner, starting with trusted machines. Monitor for new activity over the next several days.
- Enable real-time protection, enable automatic updates, and consider adding a firewall or network security appliance for ongoing protection.
- Establish a routine for regular scans, backups, and security audits to reduce reinfection risk.
- Document the incident, including affected devices and actions taken, to support future incident response.
Troubleshooting
| Symptom | Likely Cause | Fix | Prevention |
|---|---|---|---|
| Unusual system slowdowns after cleanup | Rootkit or hidden startup items | Re-scan with offline tools and check for hidden services | Keep antivirus active and schedule routine scans |
| Persistent popups or redirect pages | Browser hijack or adware tied to worm | Reset browsers, remove suspicious extensions, re-scan | Use reputable browsers and enable anti-phishing protections |
| New unknown network traffic | Worm still communicating with command-and-control | Disconnect device, re-scan with offline tool, review firewall logs | Segment networks and monitor outbound traffic |
| Unable to boot from USB recovery medium | BIOS/UEFI settings or USB protection | Enter BIOS, enable legacy/UEFI boot from USB as required | Keep backup recovery media handy |
| Antivirus reports but removal fails | Rootkit or deeply embedded malware | Use a combination of tools and perform a clean reinstall if necessary | Maintain offline backups and verify clean images |
Common Mistakes
- Relying on a single security tool; worms can hide in multiple places.
- Not disconnecting infections before cleaning, allowing spread to other devices.
- Ignoring updates and continuing to use compromised credentials.
- Assuming all malware removal tools are equally effective on every system.
Tips For Best Results
- Keep a bootable recovery USB ready for emergencies and store it offline.
- Run scans in Safe Mode when possible to avoid worm interference with security tools.
- Document all actions taken during cleanup to aid future troubleshooting.
- Regularly back up important data to offline storage or a secure cloud service.
- Use layered security: antivirus, firewall, and network monitoring for ongoing protection.
Call A Professional
Consider professional help if you notice any of these signs: persistent rootkits, firmware-level interference, or repeated reinfections after cleanup. Seek urgent assistance for business networks, critical data, or if you are uncomfortable performing BIOS changes or handling bootable media. A pro can perform advanced rootkit scans, clean reinstall strategies, and verify system integrity.
FAQ
What is a computer worm and how does it spread?
A computer worm is a self-replicating malware that spreads across networks and devices, often exploiting software vulnerabilities or weak credentials.
Can worms be removed without reinstalling Windows?
Many worms can be removed with offline scanners and proper cleanup, but in some cases a clean reinstall of the operating system may be required.
Should I change all passwords after cleanup?
Yes. After a thorough cleanup, reset all critical accounts and update passwords, especially for administrator access and network devices.
Is a firewall enough to prevent worm infections?
A firewall adds a layer of protection, but worms can exploit software flaws and social engineering. Combine firewall defense with antivirus, regular updates, and safe browsing practices.
What tools should I use for offline scanning?
Use bootable USB-based malware removal tools and reputable antivirus software in offline mode to detect infections not visible in Windows.
How long does cleanup typically take?
Time varies by number of infected devices and complexity, but plan several hours per device for a thorough cleanup.
When should I contact a professional?
Contact a pro if infections persist after cleanup, firmware-level contamination is suspected, or business networks require expert containment.
Buying Guide
When selecting tools and devices to protect against worms, consider how each option fits your setup and risk tolerance. Important factors include size and portability of recovery media, ease of use, and compatibility with your operating system.
Key buying factors:
- Bootable recovery media durability and compatibility; ensure it supports your OS and can run offline scans reliably.
- Offline malware scanners with up-to-date definitions and robust rootkit detection capabilities.
- Malware removal tools for PC that offer multi-layer scanning, heuristic analysis, and secure quarantine.
- Network protection with firewall appliances or robust software that can monitor outbound as well as inbound traffic.
Other considerations include size and placement of hardware in your workspace, noise level for quiet operation, energy efficiency for continuous use, and controls that are intuitive for quick action during incidents. Compare products by how well they integrate into your current security stack, how often updates are released, and what kind of support is offered by the vendor. If you manage a small office, a combined suite of tools may reduce complexity while strengthening protection.