For many Americans, password fatigue is real. Moving to passwordless authentication can reduce risk and improve convenience by replacing forgotten passwords with physical security keys and biometric options. This guide explains practical steps to transition to passwordless login across devices and services, using common hardware options available in the U.S. market.
Readers will find a practical, step-by-step approach, safety notes, and troubleshooting tips to help organizations and individuals adopt passwordless methods without exposing them to common misconfigurations.
Quick Answer
Adopt a hardware-based passwordless setup by enabling FIDO2/WebAuthn on your devices, acquiring a compatible security key, and enabling biometric or Windows Hello options where available. Use a combination of a USB-C/NFC security key, a biometric USB reader, and a smart card solution for multi-factor passwordless access across devices and services.
What You’ll Need
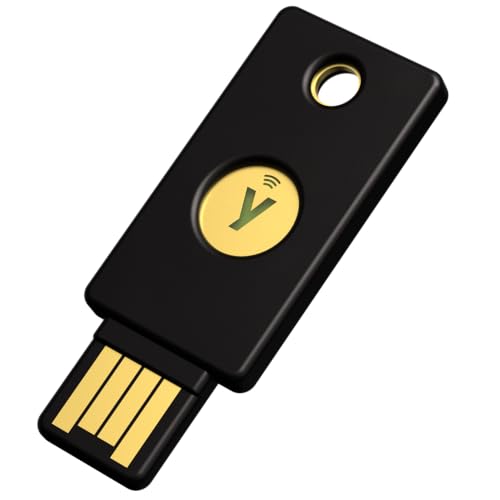
- YubiKey 5 Series USB-C NFC security key
- FIDO2 USB security key passwordless authentication
- Biometric fingerprint USB reader for Windows Mac
- Windows Hello compatible USB security key
- Smart card reader with PIN passwordless login


Before You Start
Backup current credentials and ensure you have at least one alternative recovery method in case a security key is lost or disabled. Check compatibility for your operating system, browser, and services, as features vary by platform. Prepare a safe place to store backup codes or recovery links, and ensure devices are up to date with the latest firmware and security patches. Plan for device-to-device enrollment, especially in workplaces, to avoid lockouts.
Step-By-Step: How To Implement Passwordless Access
- Audit existing accounts and identify services that support passwordless login via FIDO2/WebAuthn.
- Choose a primary security key that supports USB-C and NFC for broad device compatibility, such as the YubiKey 5 Series.
- Register the first security key with a selected account, following the service’s security settings for two-factor or passwordless authentication.
- Enable Windows Hello or biometric login on your computer if supported, and pair a biometric USB reader for additional options.
- Set up a backup authentication method, such as a second security key or a smart card with PIN, to avoid single-point failure.
- Test logging in from multiple devices and browsers to confirm seamless passwordless access across environments.
- Educate users or household members on how to use the security keys during sign-in and how to handle lost devices.
- Document recovery steps and update device policies to enforce passwordless login for supported services.
Troubleshooting
| Symptom | Likely Cause | Fix | Prevention |
|---|---|---|---|
| Cannot enroll key on a service | Service does not support the chosen protocol | Confirm WebAuthn/FIDO2 support and try another compatible key | Verify service compatibility before setup |
| Key not recognized by device | USB port issue or key needs firmware update | Try a different port; update key firmware | Keep firmware current and test on multiple ports |
| Cannot sign in after key insertion | Browser extension or policy blocking | Disable conflicting extensions; re-enroll key | Configure enterprise policies to allow passwordless |
| Forgot PIN for smart card | PIN lockout or memory lapse | Follow smart card recovery procedure; reset PIN if supported | Record PIN securely and use a backup method |
Common Mistakes
- Relying on a single security method without backups
- Using keys only on one device or browser
- Not testing recovery and fallback procedures
- Neglecting updates to firmware and system software
Tips For Best Results
Keep multiple passwordless options ready, such as a USB-C security key, NFC-enabled key, and a biometric reader, to cover different devices and scenarios. Regularly test sign-in from different apps and browsers. Store backup recovery methods securely and educate all users about how to sign in without passwords. When possible, enable passkeys for primary services to simplify enrollment and reduce phishing risks.
Call A Professional
Seek professional help if there is corporate policy complexity, larger-scale device enrollment, or regulatory requirements. If you encounter persistent sign-in failures after firmware and software updates, or if a security key is lost and recovery is unclear, contact IT support or a credentialing specialist.
FAQ
What is passwordless authentication?
Passwordless authentication uses hardware or biometric factors to verify identity without entering a password, typically via FIDO2/WebAuthn and security keys.
Are security keys compatible with Windows Hello?
Many security keys are designed to work with Windows Hello or as a standalone FIDO2 credential, enabling passwordless sign-in across apps and services.
Can I use multiple security keys?
Yes, using multiple keys provides backup access if one key is lost or damaged.
What happens if my key is lost or stolen?
Keep backup credentials and follow service recovery steps. Immediately revoke access if the device is compromised and replace with a new key.
Do all websites support passwordless login?
Not all sites support FIDO2/WebAuthn yet. Check service security settings to confirm passwordless options.
Is biometric login as secure as a security key?
Biometric options provide strong convenience, but combining biometrics with a security key strengthens protection against phishing and credential theft.
Buying Guide
When selecting passwordless hardware, consider size, compatibility, and ease of use. Key factors include:
- Size and form factor: Compact keys travel easily; some models support USB-C and NFC.
- Device compatibility: Ensure the key supports major platforms (Windows, macOS, Linux) and browsers you use.
- Security features: Look for FIDO2/WebAuthn, U2F compatibility, PIN protection, and biometric support where relevant.
- Noise level and user experience: Some keys are touch-activated; others require pressing a button. Consider how you prefer to authenticate.
- Energy efficiency and durability: Long-lasting batteries are common in some biometric readers; otherwise, USB-powered devices are reliable and durable.
- Controls and ease of enrollment: Simple setup with clear prompts reduces user friction during enrollment.
- Placement: Decide whether to place one key on a keychain, keep a spare in a safe location, or store backup credentials in a secure password manager.
For organizations, plan a phased rollout, provide user training, and establish a policy for backup methods and key management. Is passwordless the right choice for every service? Start with high-risk accounts and gradually expand as users gain familiarity and confidence.